Detecting pishing mails and mails with malware
Unfortunately, it is impossible to prevent malicious emails from reaching HTW Dresden time and again. Email addresses must be published for teaching purposes and to ensure external contact, and are therefore in the public domain.
Please delete such emails from your inbox immediately!
Malicious emails include:
- Phishing emails (identity theft): attempts to obtain users’ personal data via fake websites or emails in order to commit identity theft, obtain passwords or execute code on the computer
- Phishing emails (social engineering): Attempts to extract internal organisational information in order to identify vulnerabilities or carry out more targeted attacks
- Phishing emails (fraud): Attempts to manipulate recipients into taking ill-considered actions by exploiting a sense of authority or time pressure (disclosing passwords, purchasing and passing on gift vouchers)
- Emails containing malicious code (ransomware, Trojans, backdoors)
What should you do if it’s already happened?
If you have accidentally entered your password via a link in a malicious email, please change it immediately via the HTW website or on your domain PC. Instructions on how to change your password can be found on the ZID website.
If you have executed code via a supposed CAPTCHA, please contact the ZID as a matter of urgency.
How can you spot emails like this?
Even just one or two of the following points may be sufficient evidence of a forgery:
- incorrect or unusual sender or recipient addresses (e.g. the sender’s address is not an HTW email address but, for example, a Gmail address, even though the alleged sender is an HTW member, or your name appears in the ‘From’ field)
- Please note: even the sender’s address can be forged!! A familiar sender’s address is no guarantee of authenticity (exception: the email contains a PKI signature: S/MIME certificate)!
- The [External] label can also be circumvented
- Internal senders can be impersonated
- Similar addresses are often used (e.g. amzon.com instead of amazon.com)
- In Outlook, HTW internal senders are displayed with their surname and first name
- Make sure the tone of the message matches that of the alleged sender
- Threats of consequences are made; e.g. deletion of an email account for failing to respond within 48 hours, or pressure is applied by a purported superior
- A strong sense of urgency is conveyed
- Curiosity is piqued (the message is too good to be true)
- A meaningless or missing subject line,
- the context does not match previous correspondence (...as agreed, I am sending... even though no such agreement was made),
- no personalised greeting,
- the content is far-fetched
- Warning! Because the text can be generated or translated using AI-powered tools, it is now often perfectly worded and tailored to personal circumstances
- a fake external link (the link address appears legitimate, but the actual destination is different; this can be revealed by hovering the mouse over the link without clicking),
- no closing salutation,
- missing text signature (in a professional context, the job title and contact details are included at the bottom of the email),
- the email was sent during the night,
- errors in the official title of the recipient or alleged sender
- Attachment in .zip, Word or Excel format, or as an executable file
- missing PKI signature (in MS Outlook, an existing PKI signature is indicated by a red seal)
- On the website under ‘Guidance on signing and encrypting’, you will find detailed information on sending emails with a PKI signature and on recognising the signature
Malicious emails in a real-life context
AI tools make it easy to analyse large amounts of public data. It can also happen that partners have been compromised, and emails from you have been made public. It is therefore possible that you may receive a reply with a forged sender address in response to an email exchange that actually took place. If email correspondence is not encrypted, it can easily be intercepted. If in doubt, check via another channel (e.g. by telephone) whether the content or attachment is genuine.
Emails containing a dangerous CAPTCHA are in circulation
The HTW has received malicious emails containing a link that is not marked as [External].
The link leads to a website which uses a fake CAPTCHA to ask you to prove that you are human.
If you click on the CAPTCHA, malicious code is copied to the clipboard. The website then prompts you to run this code on your computer. This infects your computer.
Please make sure to contact the ZID or the Information Security team if you have clicked on the CAPTCHA!
Checking the email header
Überprüfung des Mail-Headers
Check in Outlook
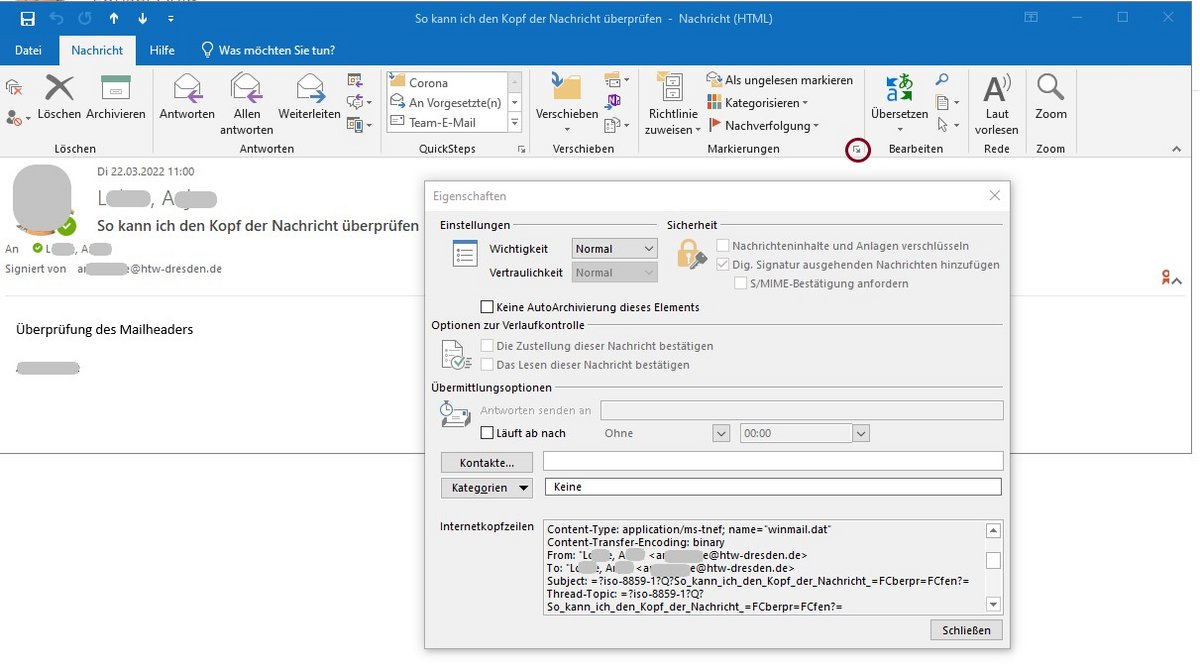
To check the header of a message in Outlook:
- Open the message with a double click
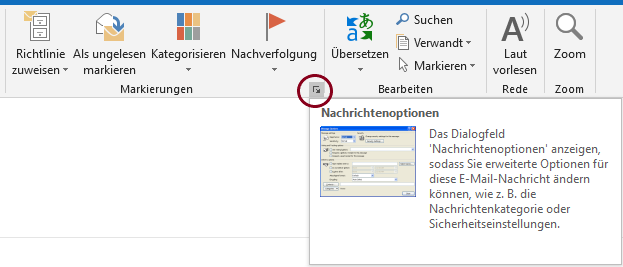
- Click on the box for message options under the item Marks.
- Under Internet headers you will now find the history of the e-mail traffic
- Pay particular attention to the Received: from and MessageID fields.
- You can find examples of forged sender addresses at the bottom of this page
Check in Thunderbird
To check the message To check the message header in Thunderbird:
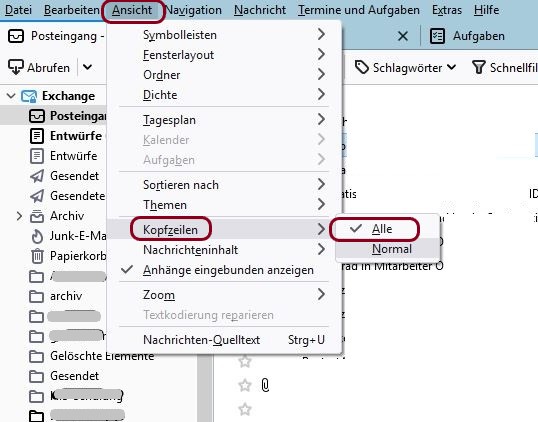
In the menu, select View --> Headers and there select All
Structure of a web address
How do you recognise a web address and its origin?
A web address has at least the following components (explained with 2 examples):
https://(1)www(2).htw-dresden(3).de(4)/(5)hochschule/organisation/rechenzentrum/arbeitsplatz-und-kommunikation/e-mail/signieren-und-verschluesseln(6)
https://(1)jobboerse(2).htw-dresden(3).de(4)/(5)jobsuche/(6)
| 1 | http:// oder https:// |
Denotes the protocol http is unencrypted, please do not submit any confidential data to the website here https is encrypted |
| 2 |
www jobboerse |
Server name, can also be composed of several parts, with .separated |
| 3 | htw-dresden | Domain, on pages of the HTW Dresden always htw-dresden |
| 4 | Land |
de=Germany <be> com=commercial* org=organisation* net=Network management* |
| 5 | / | Any information can be placed after this / |
| 6 | Directory | the directory can have any depth and any name |
*Can now be awarded to any operator
By moving the mouse over a link (no click!) the real link is displayed.
Here are three examples of a hidden link abroad:
Beispiele für gefälschte Links
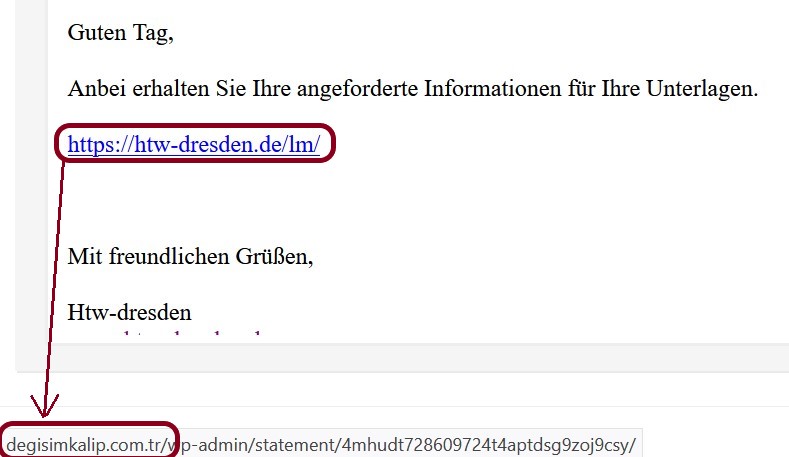
This link suggests that it is linked to the HTW-Dresden.
However, when the mouse button is hovered over, an address in Turkey is displayed (recognisable by the .tr)
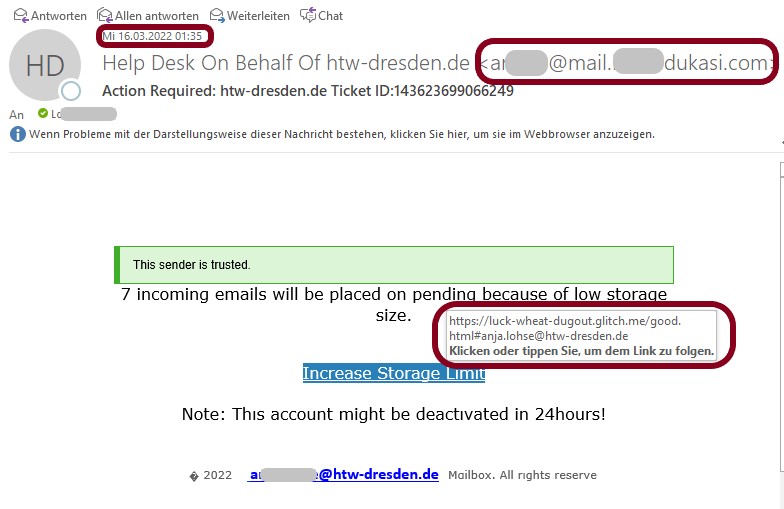
This mail has several spam characteristics:
- It was sent in the middle of the night
- It contains the threat that the account will be blocked in 24 hours and 7 mails are waiting to be read
- the sender is not from the HTW
- The link leads to Montenegro (.me)
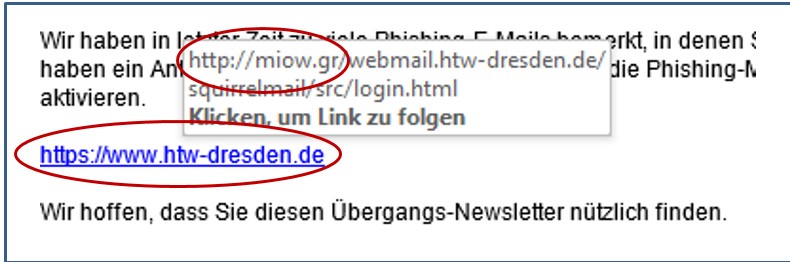
Even though in this case htw-dresden.de is included in the mail address, this is a link pointing to a web address in Greece.
All information after the first simple / designates only the directory structure and does not contain any information about the server!
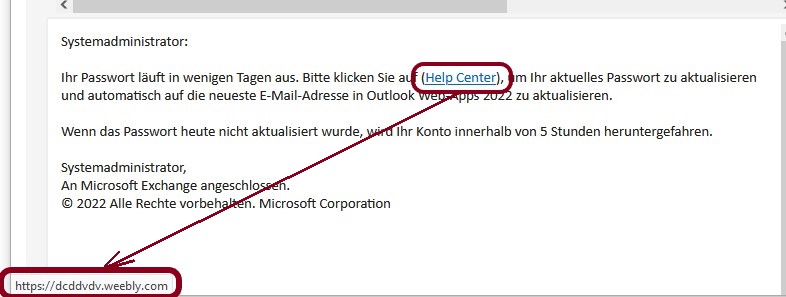
HTW Dresden will not ask you to change your login details via a link.
This link leads to a completely different website.
Always change your password by going directly to the page www.htw-dresden.de → University → Organisation → ZID (Computer Centre) → Services and Guides → Instructions for changing your password and following the method described there.
Mail header of a forged sender address
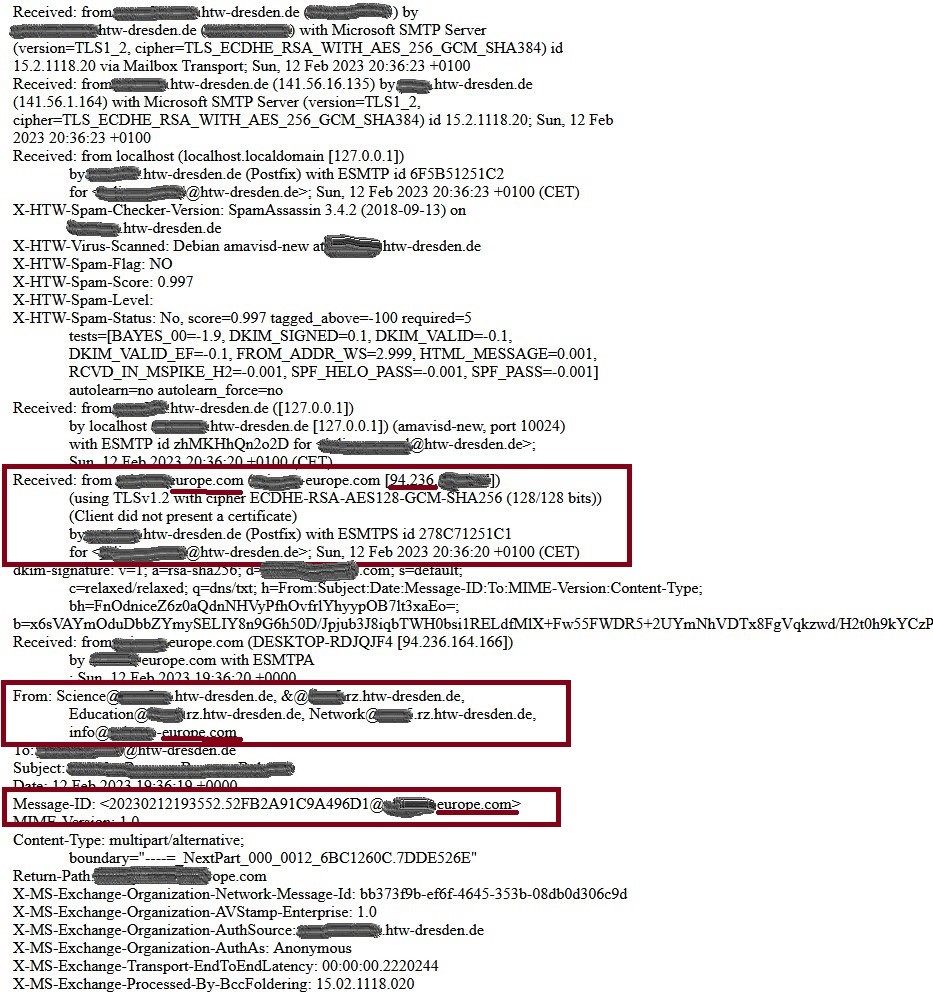
Instructions on how to access the mail header can be found at the top of this page
Here, the mail supposedly comes from an HTW mail address.
You can see from the marked entries that this mail actually comes from a server with a foreign IP and foreign server name.
Also pay attention to the MessageID entry. Here, too, it is obvious that this mail originates from a foreign server.
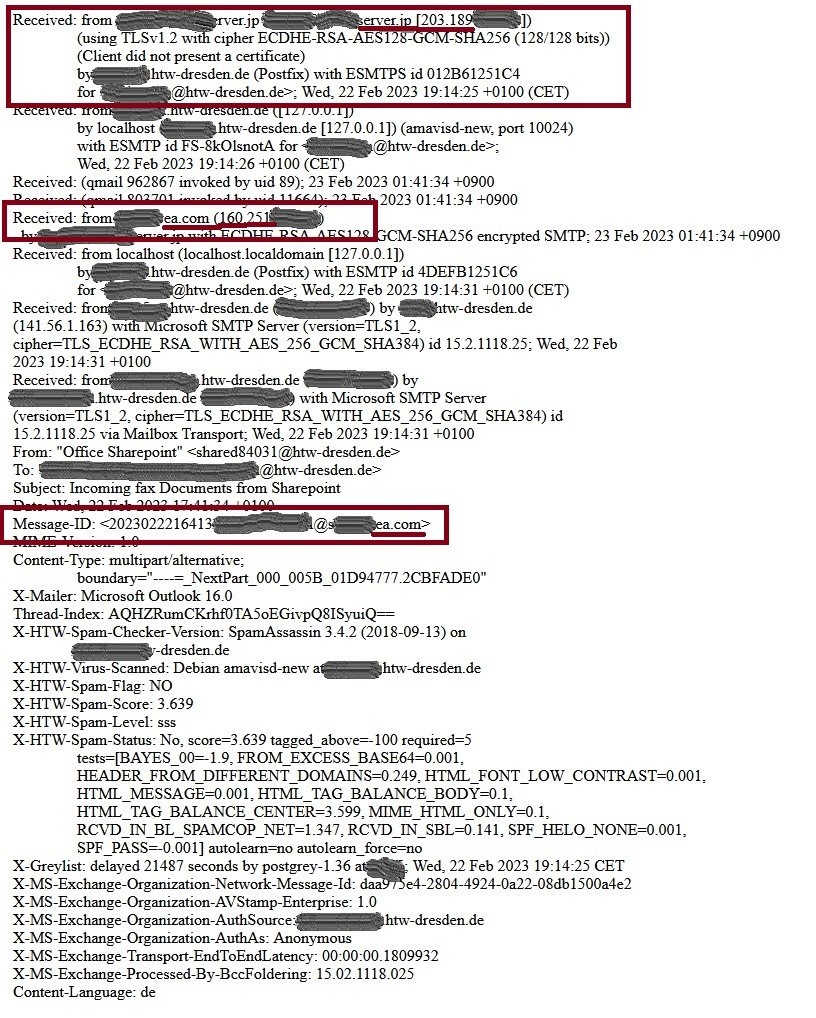
You can see from the first entry that the mail does not come from the HTW, but from Japan.
The message ID is the ID of a foreign server.